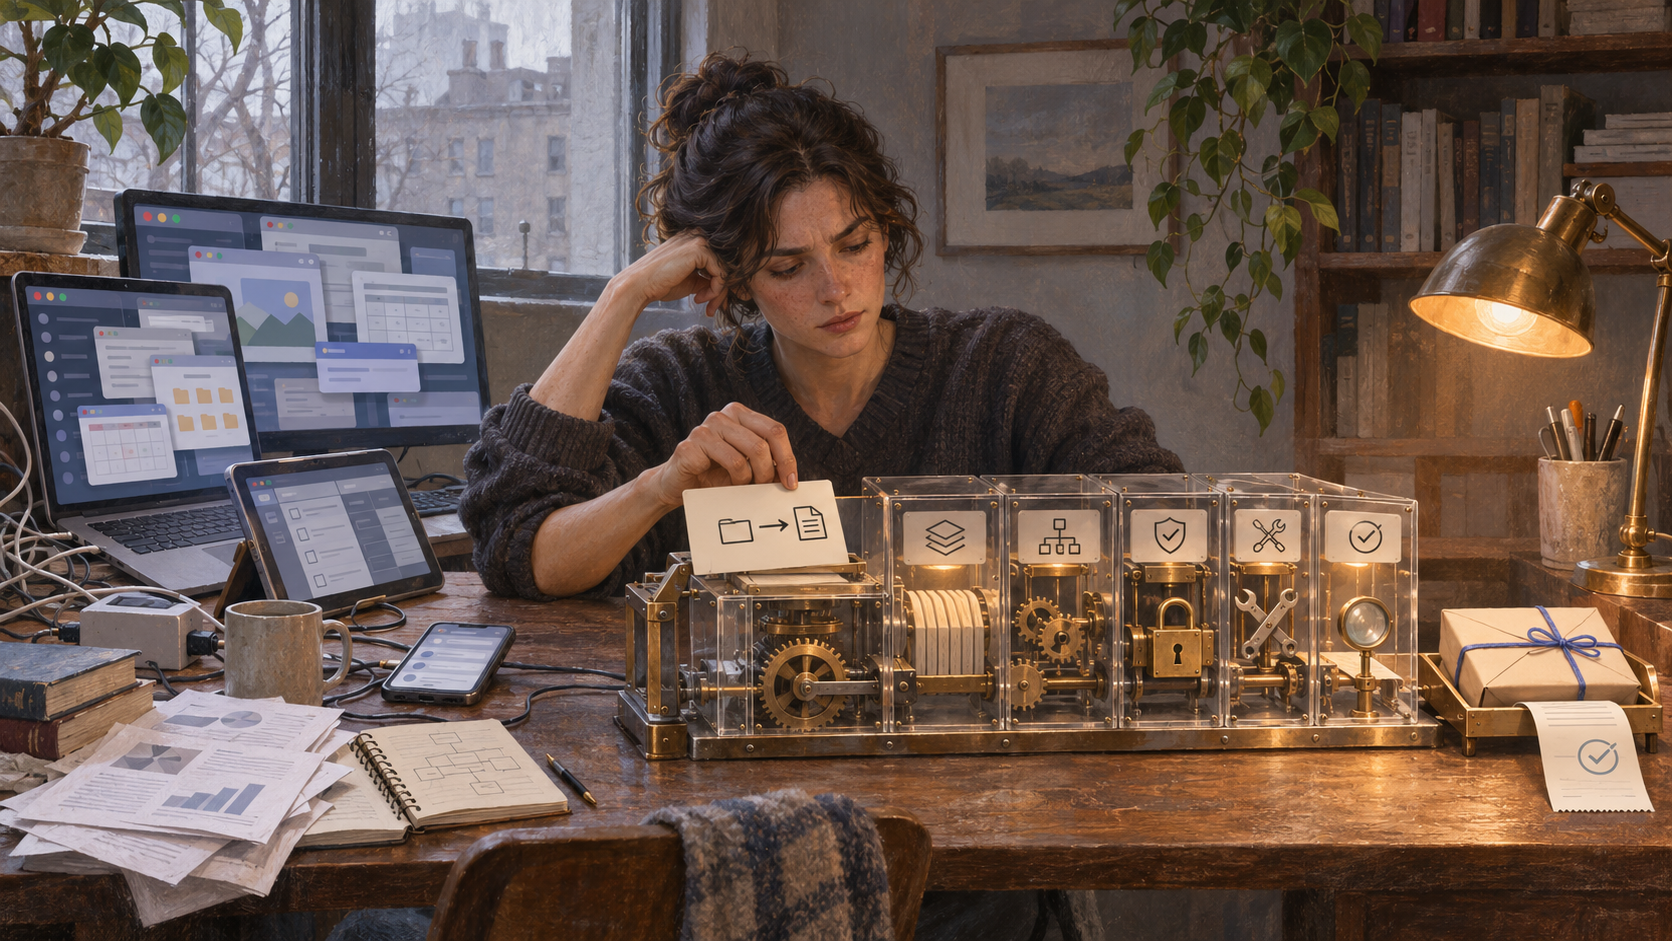
One job enters. Context, planning, authority, tools, and verification remain visible inside the machine. A result and its receipt emerge together. Illustration generated for this essay.
Six tabs for one thought
The thought arrives while I am making tea.
By the time the kettle clicks off, I have typed a sentence into my phone. I know I wrote something related three months ago, but I cannot remember whether it is in a notes app, a document, a project board, or a message to myself. On the desk, the laptop wakes into a thicket of windows.
I open the notes app and search. Nothing. I open cloud storage. Then the project tracker. Then email. I copy two fragments into a document, rename it, move one task, add a reminder, and begin a draft. Somewhere between the fourth login and the second duplicate paragraph, the original thought has gone quiet.
The job was simple:
Gather my related ideas, show me what changed, update the right records, and prepare a draft without publishing anything.
Why am I still opening apps to do that?
Apps make us navigate the software company’s map
An application is a package of capabilities, data, permissions, interface decisions, and commercial boundaries. The package made sense when software was expensive to build and distribute. A company assembled enough related features to justify installation, procurement, and maintenance. The user learned where everything lived.
That history remains visible in ordinary work. We do not move through a task; we move through the organizational map of the software industry.
The calendar company owns time. The document company owns prose. The project-management company owns status. The messaging company owns conversation. Each product gives the user a separate lobby, filing system, vocabulary, and set of tiny rituals.
To complete one human intention, I perform the integration manually:
remember where the information lives
→ open the relevant products
→ translate the goal into each interface
→ move state between them
→ reconcile conflicts
→ check whether the result is real
We call this “using software.” Much of it is unpaid orchestration.
A command is not a prompt with root access
“Software should be a command” can sound like a demand for a blank text box with unlimited authority.
That is not what I mean.
A command should be a structured agreement between a person and an execution system. It contains an outcome, the context that may be used, the actions that are allowed, the consequences that require fresh approval, and the evidence needed before the work can be considered complete.
For the writing task, the agreement might look like this:
outcome: prepare one new draft from related personal notes

context:
  read: [idea-notes, published-essays, project-journal]
  exclude: [private-messages, client-work]

allowed_actions:
  - search
  - cluster
  - quote_with_source
  - create_draft
  - propose_task_updates

must_confirm:
  - overwrite_existing_text
  - change_project_status
  - share_or_publish

completion_evidence:
  - sources_used
  - files_created
  - proposed_changes_not_applied
  - unresolved_conflicts
Natural language can begin the exchange. It should not be the only durable record of it.
The system needs to translate the request into something both sides can inspect. “Organize my ideas” is under-specified. Does organize mean rename files, merge notes, alter categories, delete duplicates, or merely prepare a suggested structure? The command becomes safe only when those ambiguities meet explicit authority.
From app navigation to an execution layer
The current model places the human above a row of products:
flowchart LR
    H["Human"] --> A["Notes app"]
    H --> B["Documents"]
    H --> C["Project tracker"]
    H --> D["Calendar"]
    H --> E["Messages"]
    A --> R["Result assembled by the human"]
    B --> R
    C --> R
    D --> R
    E --> R
The proposed model places the human above an execution layer:
flowchart LR
    H["Human intent + authorization"] --> X["Execution layer"]
    X --> C["Permissioned context"]
    X --> P["Planner and state"]
    X --> T["Tools and services"]
    X --> U["Task-specific interface"]
    C --> V["Verification"]
    P --> V
    T --> V
    U --> V
    V --> R["Completed, auditable result"]
    V -. "approval or correction" .-> H
The applications do not necessarily disappear. Their capabilities move behind a layer that can discover, combine, and operate them within the person’s authority. The human stops carrying the state of the workflow in their head.
This is closer to a standardized execution layer than to a universal super-app. It needs adapters, identity, durable task state, policy enforcement, recovery, observability, and an interface system. The language model is one component. It is not the operating system by itself.
The interface should appear when the task needs one
Not every job belongs in a chat window.
If I am comparing twelve sources, I need a table. If I am resolving scheduling conflicts, I need a timeline. If I am approving a payment, I need the recipient, amount, account, fees, and a confirmation boundary in one stable view. If the system is uncertain about whether two people are the same person, I need a side-by-side comparison—not a confident paragraph.
The interface should be assembled around the decision.
That does not require generating an entire application from scratch every time. It may mean selecting trusted components, binding them to structured tool results, and discarding the view when the task ends. Current platform work already hints at this separation: OpenAI’s developer guidance describes custom UI as optional and recommends adding it when people need to inspect, compare, edit, confirm, or navigate structured information, while keeping the underlying tool useful without the component (OpenAI developer documentation).
That principle is larger than any one platform:
Capability first. Interface when useful. Product boundary only when it earns its permanence.
The spreadsheet remains valuable because some work is genuinely spatial and iterative. The map remains valuable because geography is not improved by being described one turn at a time. The point is not to abolish interfaces. It is to stop making people visit a permanent interface merely because a capability happens to live behind it.
The plumbing is appearing
Parts of this architecture now exist in recognizable form.
Tool protocols let a model discover structured capabilities rather than improvise every integration. MCP exposes tools and resources across hosts; its authorization work increasingly uses OAuth-based boundaries and distinguishes public from protected tools (MCP Apps authorization documentation). A2A addresses coordination between agents and explicitly includes task state, long-running work, and enterprise authentication patterns (Google’s A2A announcement). Computer-use systems can operate interfaces that do not expose clean APIs.
These pieces make the direction plausible. They do not make it universal.
A protocol can describe a tool without proving that the tool is appropriate for the current task. An agent can click a button without understanding the organization’s unwritten exception. A generated dashboard can display data while quietly using the wrong definition. An authentication token can establish access without establishing that this action, now, is within the user’s intent.
Interoperability is necessary plumbing. It is not judgment, authority, or proof.
We are near compelling demonstrations, not a universal implementation
The demo version is easy to imagine.
“Plan my trip.” Windows move. Flights appear. A map opens. A neat itinerary slides into place.
The operating version is harder. Which passport? Whose loyalty account? Is the meeting movable? Is the cheapest fare refundable? Can the agent disclose dietary information to the hotel? What happens if the card is charged but the reservation callback times out? If two agents both retry, do I now own two tickets?
The distance between those scenes is where most of the engineering lives.
| Problem | A polished demo can hide | A dependable execution layer must provide |
|---|---|---|
| Identity | The agent uses the user’s session | A distinct acting principal and traceable delegation |
| Authorization | A broad “allow” button | Action-, resource-, amount-, and time-bounded authority |
| State | The happy path finishes in one run | Resumption after interruption and idempotent retries |
| Payments | A checkout page appears | Recipient binding, amount verification, fraud controls, and receipts |
| Private data | Context simply “connects” | Purpose limits, minimization, retention, and revocation |
| External failure | The tool returns success | Outcome verification against the real system |
| Conflicting instructions | The latest text wins | Source priority, policy resolution, and escalation |
| Accountability | A transcript exists | An event trail connecting intent, approval, action, and effect |
NIST’s 2026 work on software and AI-agent identity and authorization treats identification, authorization, auditing, non-repudiation, and prompt-injection controls as unresolved infrastructure questions. This is not bureaucratic decoration around the useful system. It is part of the useful system.
The execution rule should be closer to a conjunction than a confidence score:
\[\operatorname{Execute}(a) = I_{\text{intent match}} \land I_{\text{authorized}} \land I_{\text{risk bounded}} \land I_{\text{verifiable}}\]A highly confident model should not compensate for missing authority. If one condition is false, the action does not run.
Reliable operation is the unsolved center
Generating software is becoming easier. Operating software across real boundaries remains stubborn.
The system has to decide when to proceed, when to ask, when to stop, and how to recover without multiplying consequences. It must treat text inside an email, webpage, document, or tool result as information—not permission. It must distinguish “draft this” from “send this,” “find a flight” from “buy this ticket,” and “update my notes” from “rewrite my memory.”
OpenAI’s current computer-use guidance makes this boundary explicit: isolate the environment, allowlist sites and actions, keep humans in control of purchases and destructive or hard-to-reverse changes, bound time and cost, and verify the actual outcome rather than trusting the model’s final statement (computer-use guidance).
Those controls may sound less exciting than a universal assistant. They are what turn an impressive cursor into an accountable operator.
The most important system output may be a receipt:
what I understood
what I accessed
what I planned
what I changed
what I could not verify
what still requires you
Without that receipt, convenience becomes fog.
The assembly-language analogy points in the wrong direction
I have previously reached for assembly language as an analogy: perhaps apps will feel like low-level machinery once people can state outcomes directly.
That comparison needs correction.
Assembly is a programming interface close to machine instructions. It does not understand intent, choose among services, negotiate authority, or verify an external result. The more accurate comparison is compilation plus orchestration: a high-level human objective becomes a plan, the plan binds to available capabilities, policy constrains execution, and runtime evidence determines whether the requested outcome occurred.
Even that comparison has limits. A compiler receives a formal source language. Human intent arrives incomplete, contradictory, and embedded in social context. The execution layer therefore cannot merely compile. It must expose ambiguity and invite correction before consequence.
That is why the missing abstraction is not “English as code.” It is inspectable intent with bounded authority.
I have been building fragments of this idea
This argument did not begin as a prediction. It began as friction inside my own prototypes.
In Semantic Studio, I built a local compiler-lab prototype where a workflow has a typed semantic representation, validation, execution traces, generated code, semantic diffs, and version history. The useful lesson was not that natural language could produce software. It was that the intermediate representation had to remain inspectable when the prompt and the generated implementation disagreed.
In Text to Visual Breakdown, a written brief becomes an interpretation, storyboard, visual specification, and explicit assumptions. The current parser is deterministic. Its value is modest but concrete: an interface appears around one transformation, and the assumptions remain visible before production.
Life Ops is less complete. It is an integration effort across tasks, commitments, reminders, calendars, and project state. The gaps are instructive. Unified ingestion, conflict resolution, adaptive scheduling, and reliable long-running execution are precisely the places where “just connect the apps” stops being a product demo and becomes systems work.
These projects do not establish a universal execution layer. They show where the abstraction leaks.
Creating software becomes expressive; using it becomes transactional
There is a paradox here.
AI can make software creation feel more like drawing, writing, or composing. A person imagines a tool and brings it into existence because the form matters to them. Software becomes abundant, personal, and expressive.
At the same time, software use can become less attached to products. The person wants the invoice reconciled, the trip planned, the evidence compared, or the idea developed. They care about the outcome, not which application received the click.
This is the connection to AI Builders Are the New Starving Artists. When creation becomes easier, more artifacts compete for attention. The creator may care deeply about the product as an expression. The user increasingly encounters it as one temporary capability inside a larger task.
That tension does not make software worthless. It moves value toward the vision behind the capability, the reliability of its operation, the data and institutions it can lawfully reach, the trust it has earned, and the people who keep it working when the environment changes.
We may create more software than ever while thinking less often in terms of owning an app.
What I want to test with collaborators
The useful next step is not a universal assistant demo. It is a bounded comparison where failure is visible.
Choose one ordinary workflow that currently crosses three or four products: preparing a client briefing, reconciling a project plan with a calendar, organizing a research corpus, or turning an approved request into an internal operational change.
Run it two ways. In the first, a person operates the existing applications. In the second, the person issues a structured command through an execution layer with the same access. Measure completion time, corrections, permission escalations, state lost across tools, unverified claims, and the person’s ability to reconstruct what happened.
| Collaborator | First artifact |
|---|---|
| HCI researcher | A task study comparing app navigation with intent-and-review interaction |
| Identity or security engineer | A scoped delegation and revocation model for one cross-service workflow |
| Internal-tools or enterprise platform team | A sandboxed workflow with real exceptions and reversible actions |
| Protocol or agent-infrastructure builder | A portable task packet with state, cancellation, and outcome evidence |
| Designer | A small grammar for task-specific interfaces and consequential confirmation |
I am interested in research and industry partners willing to expose the awkward middle: where the command was ambiguous, where permission became too broad, where a retry threatened duplication, and where the generated interface hid the wrong thing.
If the execution layer merely replaces five visible apps with one invisible source of mistakes, it has failed.
A narrow bridge to Aegis
This essay stands on its own as an argument about personal and enterprise computing. I plan to carry one component into Aegis: the execution receipt should bind a human-approved intent to the agent identity, delegated authority, tool calls, verification evidence, and observed effect. Aegis can improve by evaluating that chain without becoming the universal execution layer itself.
The command after the kettle clicks
The tea has gone cold beside the laptop.
In the current world, I reopen the six tabs and continue reconstructing the task from their menus. In the proposed world, I state the outcome, inspect the sources and limits the system inferred, narrow one permission, and let it prepare the work. When it finishes, I receive the draft and the receipt together.
No magic. No invisible root access. No claim that a model understood my life because it moved a file correctly.
Just a quieter relationship with software:
Here is what I need. Here is what you may use. Here is what you may change. Show me what happened.
Software should meet the person at that sentence.
Sources and limits
- This is an opinion about interface direction, supported by prototypes and emerging standards. It is not a claim that a safe universal execution layer exists.
- MCP, A2A, computer-use systems, and dynamic UI components solve different parts of the stack. Their presence does not establish end-to-end reliability.
- The project examples are my own prototypes with the implementation boundaries stated above; they are not evidence of general adoption or measured productivity gains.
Related essays
- REA Is Not Really About Reverse Engineering asks what happens when application boundaries weaken and capabilities become portable.
- The End of Programming as the Primary Interface develops the inspectable-intent and behavioral-evidence architecture in technical detail.
- Personal Intelligence Arrives as Permission, Not AGI examines the authority ladder for systems that act on longitudinal personal context.
- The Internet’s Next Protocol Layer maps the emerging coordination and transaction standards behind agentic systems.
After the last line
Comments & sharing
Agree, disagree, add context, or send this to someone who would have a take.
Share
Public thread
Comments are public and attached to this post through GitHub Discussions. Sign in with GitHub to join the thread.
Open public discussions